Open-Source AI Fuels New Wave of Blockchain-Based Malware Threats
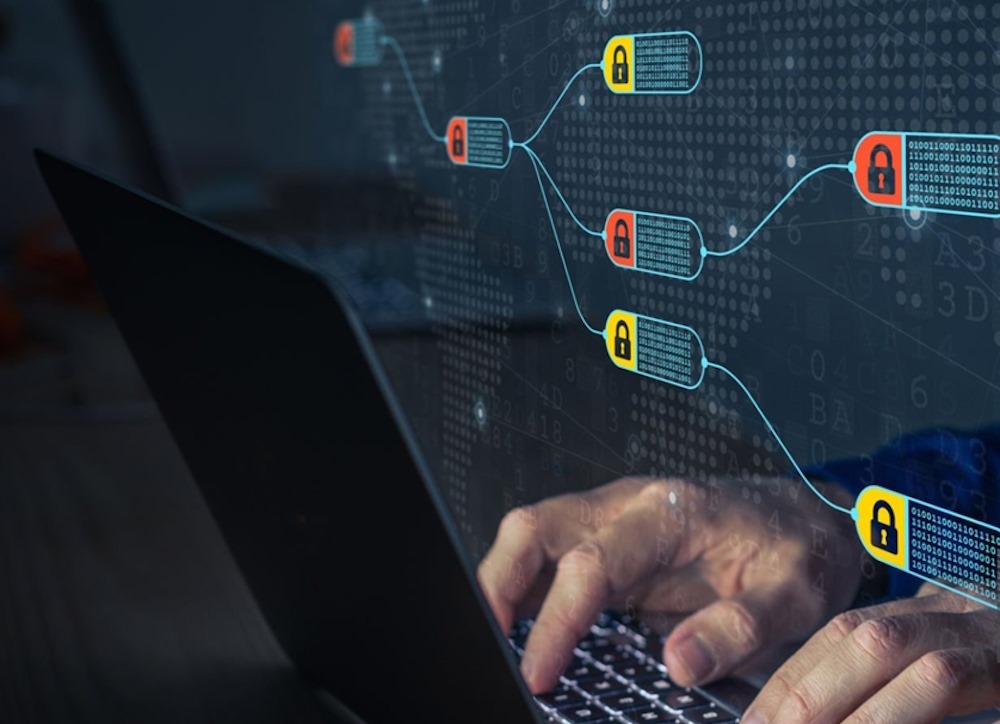
The already troubled cryptocurrency sector is confronting a new threat from open-source AI, which makes it easier to hide dangerous code on blockchains. A research was published on Thursday stating that the number of instances of malware instructions encoded in on-chain transactions and smart contracts has increased by an astounding 440% in the last year, with an average of 11 occurrences per day. Before strong Chinese open-source AI models were released in the middle of last year, the research claims that such occurrences averaged two per day and could generate harmful code without constraints. Malicious software (malware) is used in a malware attack to steal data, credentials, or money from a computer or network. The report details assaults where hackers use a technique called a “blockchain dead drop” to insert software instructions into a blockchain, along with the location of the server that controls it. Since data recorded on a blockchain is not easily removable, this can make attempts to stop an attack more difficult.
“When malware uses a blockchain to relay key information – for example, where to find its latest active command-and-control server – its attempts to reconnect with the attacker become much harder to block effectively,” stated Vitaly Kamluk. According to the report, the bulk of this activity is currently being carried out by state-backed entities, namely those linked to North Korea and Iran. When it comes to countries where acquiring hosting services or renting servers could lead to security investigations or financial transaction problems, Kamluk claims that blockchains could entice state-affiliated entities. Based on the results, it seems like generative AI is helping hackers launch more attacks and locate more software vulnerabilities, both of which are contributing to a rise in cyber risks. According to blockchain intelligence firm TRM Labs, the number of hacks in the cryptocurrency arena increased by almost 150%, hitting 207 in the first half of the year.
According to Eric Jardine in an email answer to queries, blockchains are typically not involved in the initial penetration of a machine. This typically happens through more conventional means, such as supply-chain attacks or destructive downloads. According to him, the company can’t tell how many attacks were successful or how much money was lost because blockchain data doesn’t provide that information. Chainalysis asserts that the idea of malware being concealed within blockchain technology is not new. But now that sophisticated open-source AI models are appearing, thieves can launch more widespread attacks. These risks are getting more complex, and state actors are getting involved more and more.
An even greater concern is that open-source AI models can be run independently, giving cybercriminals the opportunity to change or remove cybersecurity measures. “This gives malicious developers greater control over the model and more privacy, because they do not have to submit their source code to large cloud providers that may monitor their platforms for abuse,” Kamluk stated. Google, owned by Alphabet Inc., and OpenAI, another company, can limit access to their AI services when they detect misuse. However, blockchains’ transparency isn’t without its drawbacks. Chainalysis points out that investigators may permanently record every update attackers publish, which helps them to map their infrastructure and connect campaigns that might seem unrelated at first.